Certbot Alternative: When to Keep Certbot and When to Switch
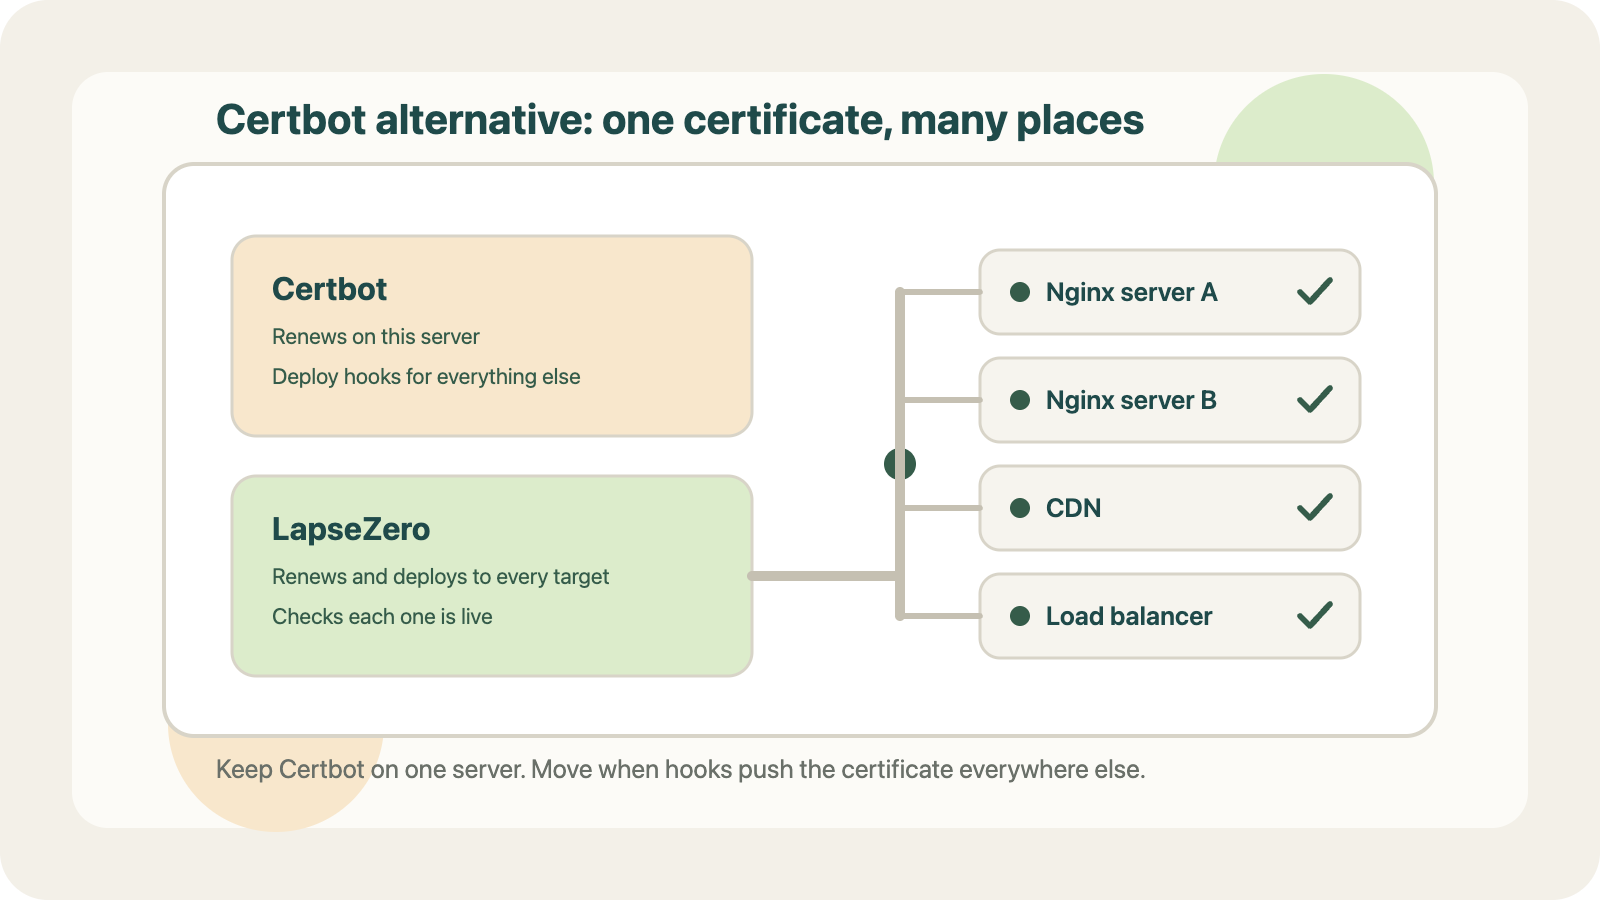
Certbot is the ACME client most people start with, and for good reason. It is free, maintained by the EFF, and it is what Let's Encrypt recommends to most people with shell access. Install it, run it
Responses
Markdown supported · ⌘↵ to post
Edge Ops
Solid framing on when a single-box Certbot flow is enough. In practice I keep nginx as the TLS terminator and reverse proxy when everything lands on one edge host: A/AAAA (or a short TTL CNAME) must already resolve before HTTP-01, then Certbot’s nginx plugin rewrites the server block and renewal is just a timer plus
nginx -ton reload. Pain shows up with wildcards or multi-node edges—switch to DNS-01, share the cert (or terminate TLS once at the edge), and put proxy cache + cache-control in front of the origin so you are not reissuing or reloading on every box.