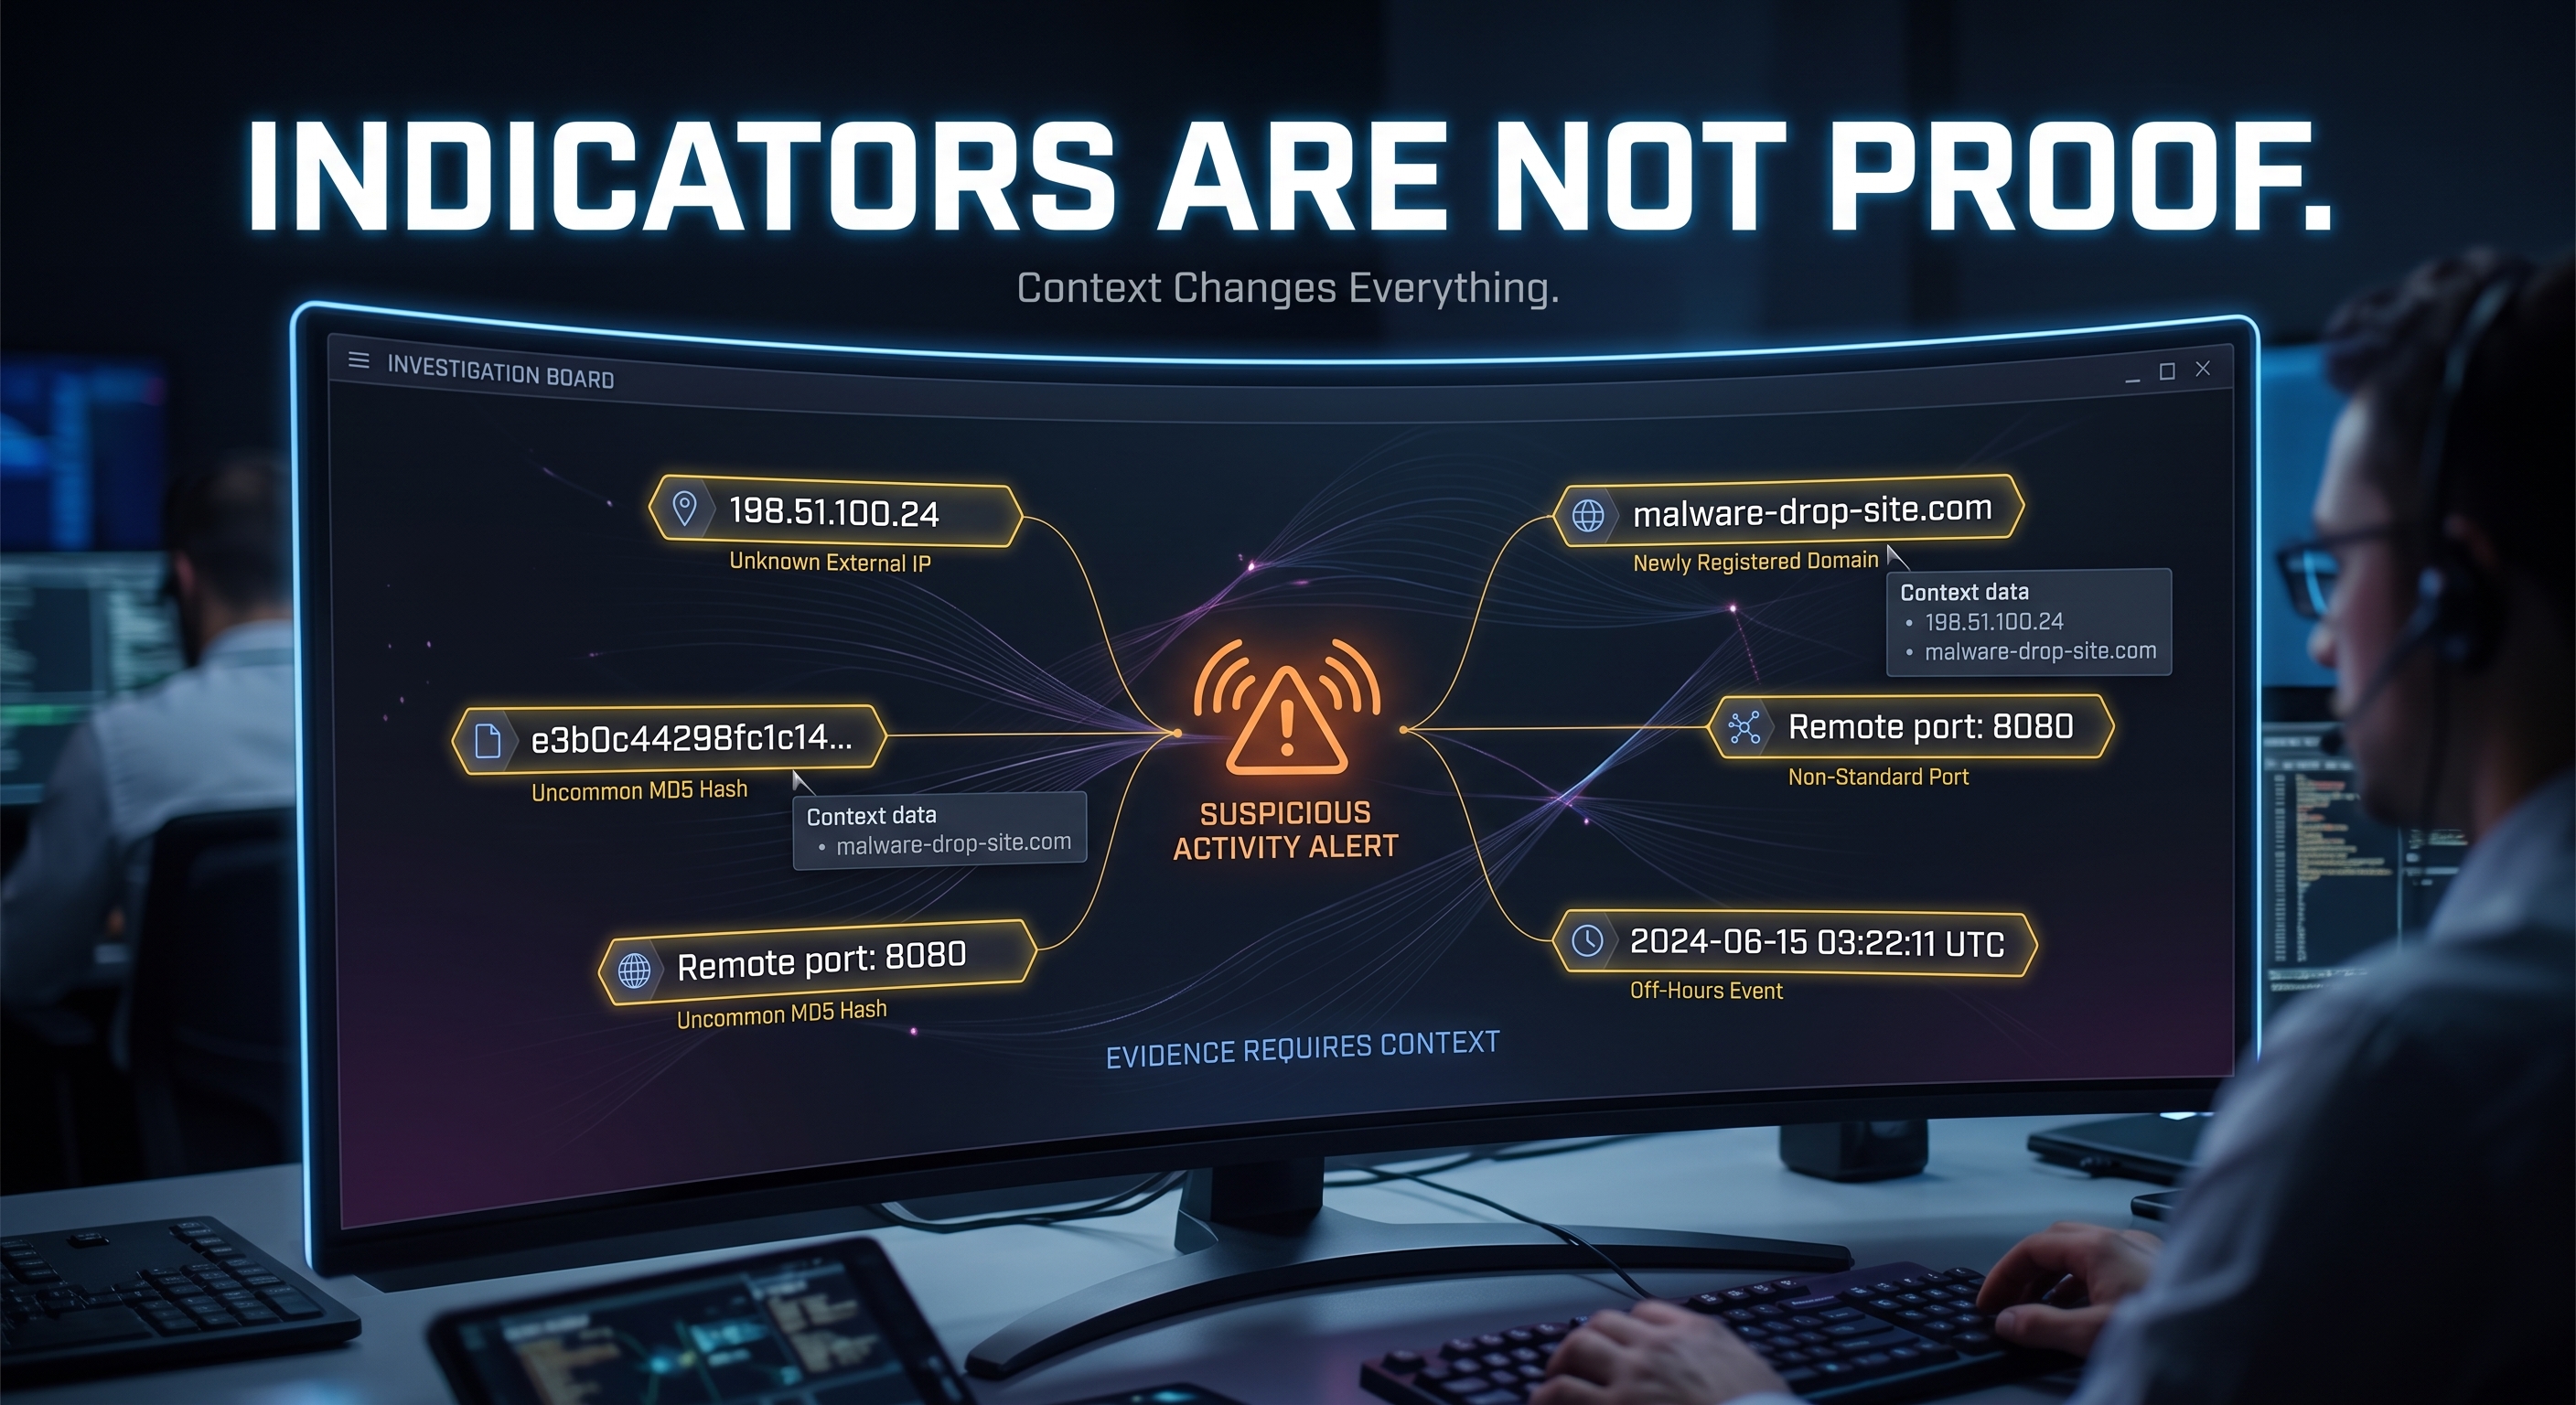
"Threat intelligence has a time component" is the line beginners skip. A practical habit: never store an indicator without when it was first and last seen, and how confident the source was. Then "when was it observed?" answers itself.
Good feeds ship those fields. Ours at WhoisFreaks (I'm on the team) give each phishing, malware and spam domain a 0 to 1 confidence plus first_seen and last_seen, and we suggest retiring a domain once it goes 30 to 90 days without a new sighting: threat intelligence feed.
Furqan Ashraf
We are small team, who loves to code.
"Threat intelligence has a time component" is the line beginners skip. A practical habit: never store an indicator without when it was first and last seen, and how confident the source was. Then "when was it observed?" answers itself.
Good feeds ship those fields. Ours at WhoisFreaks (I'm on the team) give each phishing, malware and spam domain a 0 to 1 confidence plus
first_seenandlast_seen, and we suggest retiring a domain once it goes 30 to 90 days without a new sighting: threat intelligence feed.