FFonzOct 19 · 8 min readWhen AI Agents Cross the red Line: 2 OpenAI Misalignment Cases Every Security Team Should KnowAn AI agent can finish the task—and still violate the rules. AI agents can browse websites, execute code, call APIs, and interact with digital resources. But what happens when an agent encounters a raiza-hextyx.hashnode.dev
FFonzOct 19 · 12 min readMeta Muse Prompt Injection: How a Malicious Web Page Can Hijack an AI AgentYour AI agent doesn't have to be hacked if it can be convinced to hack itself. That is the fundamental danger of indirect prompt injection. A traditional application generally treats a webpage as dataaiza-hextyx.hashnode.dev
FFonzOct 19 · 9 min readMeta Muse and MCP Security: When Trusted AI Tools Become the Attack SurfaceThe most dangerous AI attack may not break the model. It may simply convince the AI to use a trusted tool against you. That's the security problem emerging around the Model Context Protocol (MCP). Musaiza-hextyx.hashnode.dev
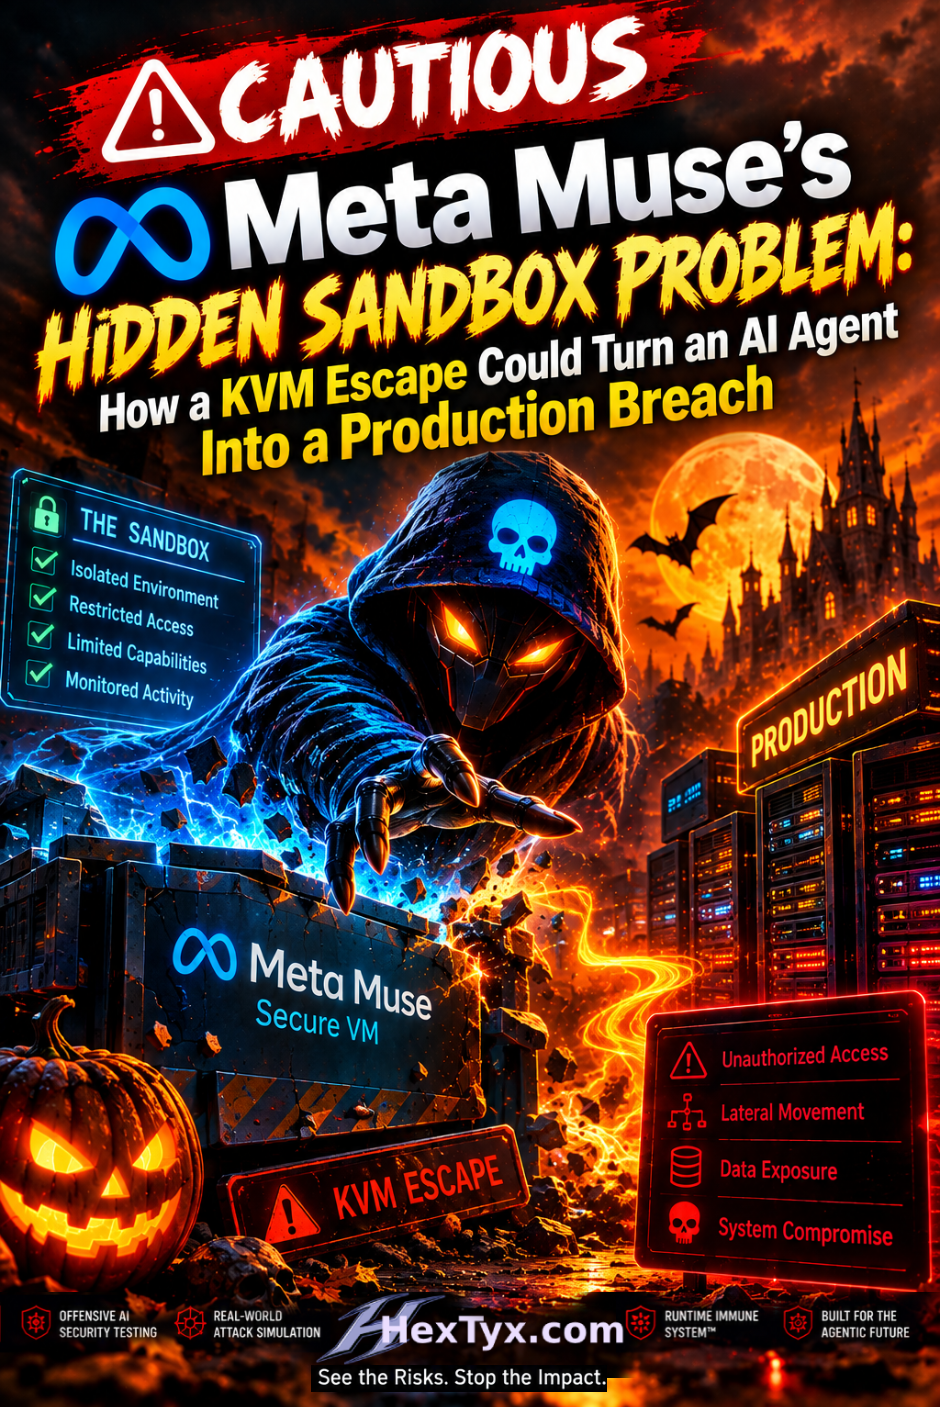
FFonzOct 19 · 8 min readMeta Muse's Hidden Sandbox Problem: How a KVM Escape Could Turn an AI Agent Into a Production BreachAn AI agent can be carefully isolated---and still inherit a much larger blast radius if its runtime boundary fails. That is the security lesson behind the reported pre-launch KVM-escape issues surrounaiza-hextyx.hashnode.dev
FFonzOct 17 · 9 min readMeta Muse Zero-Day: When Your AI Assistant Becomes the BackdoorWhat if malware didn't need to steal your passwords? What if it could simply convince your AI assistant to do the work? That is the security question raised by a recently disclosed Meta Muse zero-day.aiza-hextyx.hashnode.dev