HHareeshwar N K1d ago · 6 min readWhen the Database Talks Back: Blind SQLi Data Exfiltration Over DNSTL;DR Target/Lab: PortSwigger Web Security Academy, Blind SQL injection with out-of-band data exfiltration — Practitioner, CWE-89, solved in an authorized lab instance. Vulnerability class: Blind SQLhareeshwarnk.hashnode.dev
4404 Founders2d ago · 5 min readOracle EBS CVE-2026-101767: Unauthenticated SQL Injection That Chains to RCEA crafted unauthenticated request to the Thin Client Framework servlet gives an attacker SQL execution as the APPS database user, and the attack chain goes on to operating system commands. Probing sta404-founders.com
YYogeshwar PeelaOct 12 · 8 min readTryHackMe: PlottedTMS WriteupSummary Plotted is a Linux CTF box hosting a PHP "Traffic Offense Management System" (TOMS) admin panel across two web services (ports 80 and 445). Initial enumeration uncovered decoy files and a leakexploitnotes.hashnode.dev
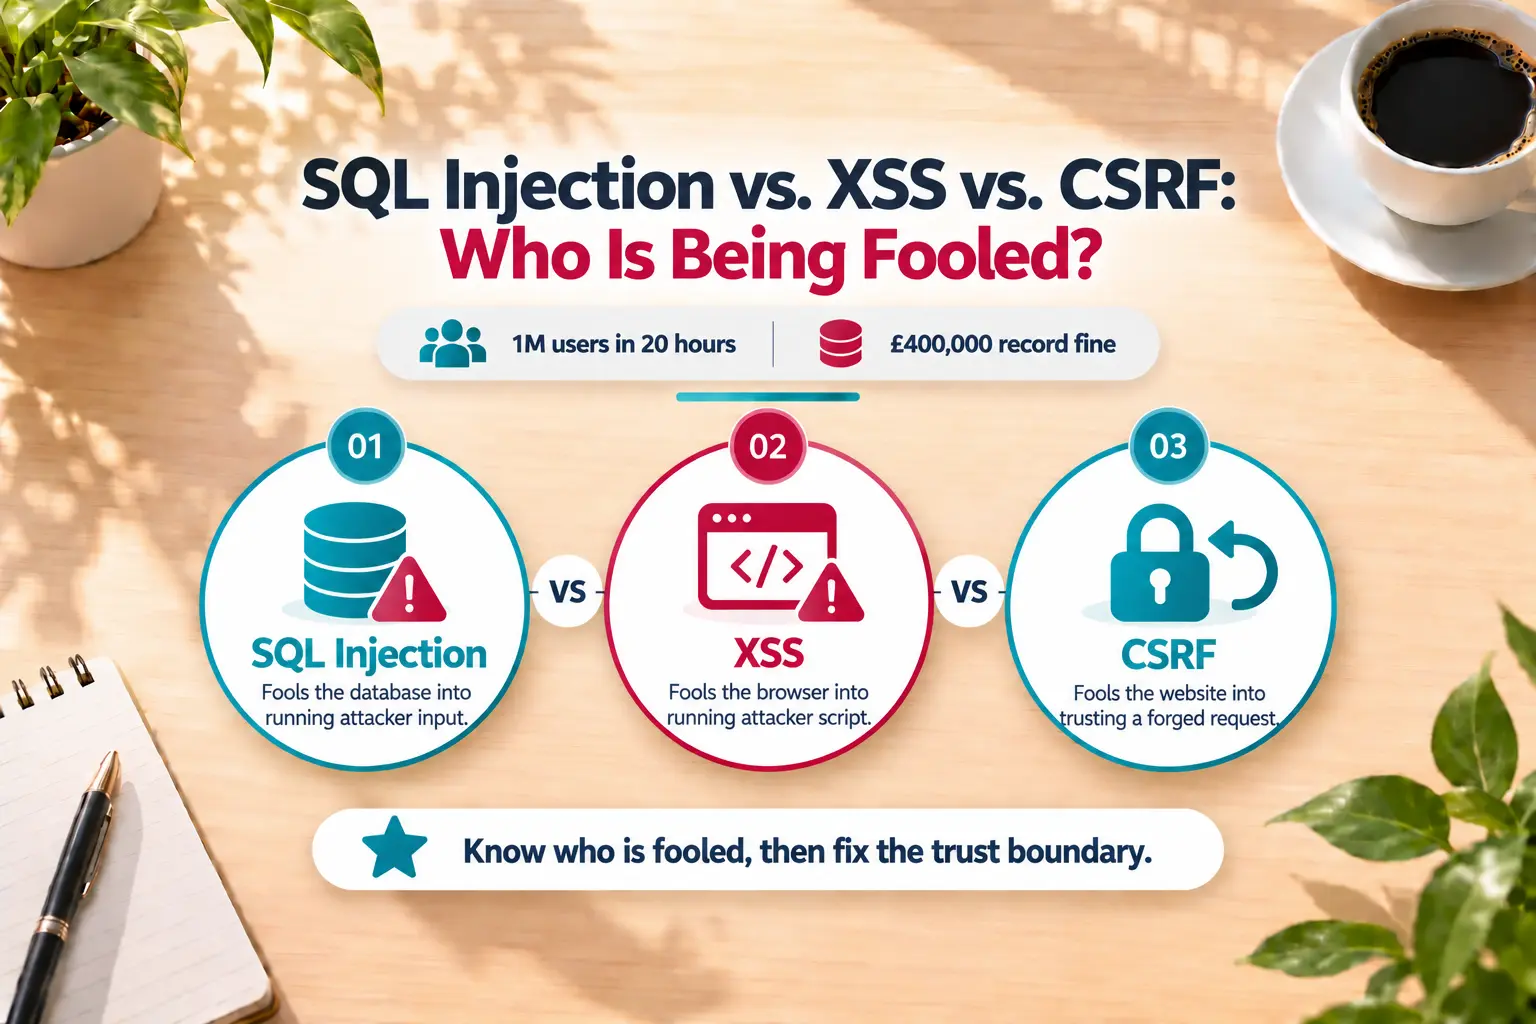
CCiphemic academiaOct 13 · 15 min readSQL Injection vs. XSS vs. CSRF: 1 Million Users in 20 Hours and a £400,000 FineSQL Injection vs. XSS vs. CSRF: 1 Million Users in 20 Hours and a £400,000 Fine On October 4, 2005, a MySpace user posted a profile containing a few lines of JavaScript that slipped past the site's ficiphemicacademia.hashnode.dev
YYogeshwar PeelaOct 12 · 7 min readTryHackMe: Gallery WriteupSummary Gallery is a Linux box running a "Simple Image Gallery System" PHP application on port 8080. The login form is vulnerable to a classic SQL injection auth bypass, which grants admin access. Theexploitnotes.hashnode.dev
TTrust BoundaryOct 12 · 12 min readAI agents broke into 27 online shops for $25 a companyOriginally published at trustboundarystudio.com. The video version, with diagrams, is on YouTube. Key facts When: Campaign running since July 2026 and still active at publication. Gambit Security's wtrustboundarystudio.hashnode.dev
IIliyaSep 29 · 8 min readIntigriti September 2026 Challenge, Critter GalleryVulnerability: Unauthenticated SQL injection (MySQL 8.0.46) in the base64-encoded pic parameter of /challenge.php, exploited with a single-column UNION SELECT to read the secret_vault table. TL;DR /cblog.iliyadindar.site
4404 FoundersSep 28 · 2 min readRoundcube CVE-2026-48842: Pre-Auth SQL Injection ExploitedRoundcube CVE-2026-48842: pre-auth SQL injection is being exploited CVE-2026-48842 is a pre-authentication SQL injection in Roundcube Webmail's optional virtuser_query plugin. Roundcube fixed it in ve404-founders.com
YYogeshwar PeelaSep 10 · 10 min readTryHackMe - Olympus WriteupSummary Olympus is a Linux box built around an old Victor CMS 1.0 install hidden under /~webmaster/. An unauthenticated SQL injection in the CMS search feature was the root of the entire chain: it dumexploitnotes.hashnode.dev
ZZeroProtocolAug 13 · 7 min readCommon Web Application TechnologiesIntroduction Modern web applications are rarely built with a single technology. A typical application combines a web server, a programming language, a framework, a database, data formats, and backend 1webpentestingdeepdive.hashnode.dev